
What Does siem monitored 24x7 by a soc Really Cost to Operate?
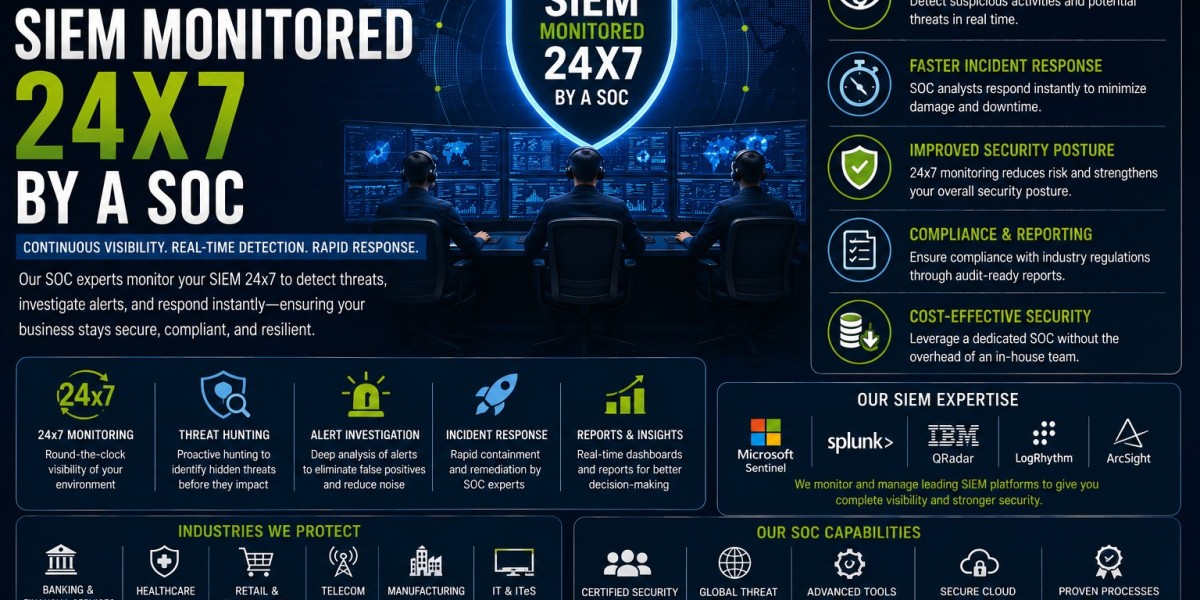
For banks, financial institutions, insurance organizations, and other BFSI businesses, cybersecurity monitoring cannot be treated as an occasional IT activity. Security events can emerge at any time across applications, networks, endpoints, identities, and digital services. siem monitored 24x7 by a soc provides a continuous operating model in which SIEM technology collects and analyzes security information while SOC professionals monitor and investigate relevant events.
The cost of this model is not determined by one universal rate. It depends on the environment being monitored, the amount of security data involved, required coverage, operational responsibilities, and the level of security expertise needed.
What Determines the Cost of siem monitored 24x7 by a soc?
The cost of a 24×7 SIEM and SOC arrangement is primarily influenced by the scope and complexity of monitoring rather than by the SIEM label alone. Organizations need to consider what they want monitored, how much security data is generated, how alerts will be investigated, and what operational support is expected.
For BFSI organizations, this distinction is particularly important because a financial environment can contain numerous interconnected systems and sensitive business processes. A low-cost monitoring arrangement may not provide meaningful value if critical sources or operational responsibilities are excluded.
Understanding managed soc pricing for BFSI Organizations
managed soc pricing can vary because managed security services are generally designed around the customer's environment and service requirements. Factors such as monitoring scope, security data volume, technology requirements, analyst involvement, service coverage, and response processes can influence the overall commercial model.
BFSI decision-makers should therefore avoid comparing providers only by headline pricing. Two services with apparently similar prices may deliver very different monitoring coverage or operational responsibilities.
A more useful approach is to evaluate the security outcomes included within the proposed service and then compare the total operational value.
Technology Is Only One Part of the Cost
A common mistake is to view SIEM expenditure as the complete cost of continuous monitoring. The technology is only one component of a functioning security operation.
A practical 24×7 model may involve:
- SIEM technology and associated configuration
- Integration of relevant security data sources
- Security event collection and analysis
- Alert monitoring and investigation
- Security analyst expertise
- Escalation and communication procedures
- Incident investigation support
- Reporting and operational visibility
- Ongoing tuning of monitoring logic
The balance between these components depends on the organization's security requirements.
For BFSI organizations, understanding the full service scope is more useful than focusing on one technology or licensing component.
Why DIY 24×7 Monitoring Can Become Expensive
Building a security monitoring function internally can appear attractive because the organization retains direct control over its people and processes. However, continuous operations require more than purchasing a SIEM platform.
An internal model may require security professionals with different areas of expertise, appropriate operating procedures, alert-handling processes, training, and coverage outside standard working hours.
Staffing is also only one consideration. The organization needs to establish how alerts are prioritized, who investigates them, who communicates incidents to stakeholders, and how monitoring quality is maintained over time.
For some BFSI organizations, an external SOC model can provide a way to access dedicated monitoring capabilities without creating every operational component internally.
The Role of Monitoring Scope in Cost
Monitoring scope is one of the most important questions to clarify during a commercial evaluation.
A BFSI organization should understand exactly which environments are included. Depending on the agreed architecture, these may include network infrastructure, endpoints, applications, identity systems, cloud environments, and other relevant security sources.
Adding more sources can increase the volume and complexity of security information that must be processed. However, reducing coverage simply to lower the service cost can create blind spots.
The right question is therefore not "What is the cheapest monitoring option?" It is "What level of monitoring provides appropriate visibility for our environment?"
Security Data Volume Matters
SIEM platforms process security information generated by connected systems. The amount of data entering the platform can influence technology and operational requirements.
A larger environment may generate significantly more events than a smaller one. But volume alone does not determine security value. Effective monitoring requires meaningful data, appropriate filtering, useful correlation, and analyst attention.
BFSI organizations should ask how the proposed service handles data sources, event volumes, alert prioritization, and unnecessary noise.
This helps prevent an organization from paying for large quantities of security data without receiving proportional operational value.
Compare Service Value Instead of Price Alone
When evaluating a 24×7 SOC arrangement, procurement and security teams can use a structured comparison.
Cost and Value Factor | Questions to Evaluate |
Monitoring coverage | Which systems and security sources are included? |
SIEM operations | Who manages configuration, correlation, and monitoring logic? |
Analyst coverage | Who reviews and investigates security alerts? |
Availability | What level of continuous monitoring is provided? |
Escalation | How are significant events communicated to the BFSI organization? |
Incident support | What assistance is available when suspicious activity requires investigation? |
Reporting | What operational and security information is provided? |
Scalability | Can the service accommodate changes in the monitored environment? |
Service scope | Which activities are included and which remain the customer's responsibility? |
This approach helps organizations compare actual capabilities rather than simply comparing commercial figures.
The Hidden Cost of Security Blind Spots
The financial impact of cybersecurity is not limited to the cost of a security service. Gaps in monitoring can create operational and business risks.
If suspicious activity is not identified promptly, an organization may have less opportunity to investigate and contain it. The potential consequences can include operational disruption, investigation requirements, recovery work, reputational concerns, and regulatory obligations depending on the incident.
That does not mean every security event will produce a financial loss. Rather, continuous monitoring can be viewed as part of an organization's broader risk-management strategy.
For BFSI businesses, where trust and availability are particularly important, security visibility has value beyond the monitoring invoice.
When an External SOC Model May Make Sense
An external SOC can be considered when an organization requires continuous monitoring but does not want to establish every element of a dedicated internal security operation.
It may also be relevant when internal security personnel need additional operational support or when the organization wants dedicated attention to security monitoring alongside its existing technology teams.
The decision should be based on business requirements, risk tolerance, existing capabilities, technical architecture, and the organization's ability to manage security operations internally.
There is no universal model that is appropriate for every BFSI organization.
A Practical Cost-Evaluation Checklist
Before approving a 24×7 SIEM and SOC service, BFSI decision-makers should verify:
- The systems and environments requiring monitoring are documented.
- Security data sources are clearly identified.
- The expected monitoring coverage is defined.
- Alert investigation responsibilities are established.
- Escalation procedures are documented.
- Service boundaries between the SOC and internal teams are clear.
- Reporting requirements are agreed.
- The organization understands how changes to its environment affect service requirements.
- Security and compliance responsibilities are considered during procurement.
- Commercial comparisons are based on equivalent service scope.
Compliance Should Be Part of the Commercial Discussion
BFSI organizations should consider cybersecurity monitoring alongside their applicable regulatory, security, and governance responsibilities. Depending on the organization and its activities, requirements from Indian financial-sector regulators and broader information-security frameworks may influence how security events, logs, incidents, access, and controls are managed.
Organizations using ISO 27001-aligned practices should also consider how monitoring and incident-management processes fit into their wider information security management system.
The specific requirements applicable to a business depend on its regulatory status and operations. A SOC service should therefore be evaluated as part of the organization's broader security and governance framework rather than as an isolated technology purchase.
Making the Investment Decision
The most effective way to assess 24×7 SOC monitoring is to look beyond the initial service cost. BFSI organizations should examine the coverage they receive, the expertise available, the operational workload transferred or shared, and the visibility gained across their security environment.
IBN Technologies provides cybersecurity services including SIEM & SOC capabilities designed to support organizations with security monitoring and operational security requirements.
For BFSI decision-makers, the objective should be a sustainable security operation that provides meaningful visibility without creating unnecessary complexity. siem monitored 24x7 by a soc can become a valuable part of that model when its scope, responsibilities, monitoring coverage, and commercial terms are clearly defined before implementation.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - [email protected]