
What to Examine Before Investing in SOC Managed Service Providers
Financial institutions operate in an environment where digital services, customer information, payment systems, applications, and internal infrastructure all require careful security oversight. For Indian BFSI organisations, security monitoring therefore needs to support more than technology visibility. It needs a clearly defined operational process for identifying, investigating, and escalating potentially harmful activity.
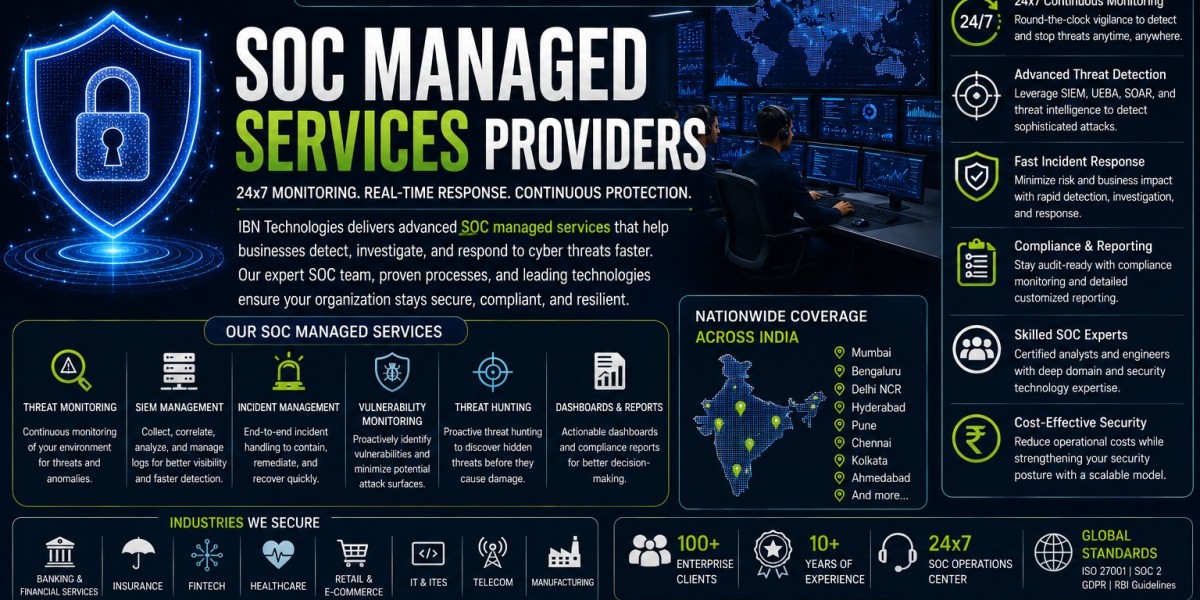
This is why soc managed service providers are increasingly relevant to organisations assessing how to strengthen security operations. A managed Security Operations Center can provide monitoring and specialist operational support without requiring the organisation to independently build every element of a SOC.
However, selecting a service should begin with understanding the organisation's actual security requirements rather than simply looking for a provider with a long list of capabilities.
Why BFSI Organisations Need a Structured Security Monitoring Model
A financial organisation can have numerous security events occurring across its technology environment. Authentication activity, endpoint events, network activity, application events, and other security signals can all contribute to the organisation's security picture.
The challenge is determining which events deserve investigation.
A managed SOC provides an operational framework for collecting relevant security information, analysing alerts, investigating suspicious activity, and escalating significant findings according to defined procedures.
For BFSI organisations, this structure can help connect security monitoring with wider security governance and incident-management processes.
The objective is not to eliminate every security event. It is to establish a repeatable method for identifying activity that may require attention.
How Top SOC as a Service Providers Should Be Assessed
When organisations search for top soc as a service providers, the evaluation should focus on service capability rather than the label itself.
A provider's suitability depends on factors such as monitoring scope, analytical processes, incident escalation, reporting, integration, security expertise, and alignment with the customer's operating environment.
For a BFSI organisation, these considerations should be assessed against the systems and information that are genuinely important to the business.
A provider that understands how its service will connect with the customer's existing security and IT responsibilities can offer a more clearly defined operating model.
The evaluation should therefore ask not only what the provider offers, but also how those capabilities function during day-to-day monitoring and during a security incident.
Where Security Monitoring Can Break Down
Security gaps do not always result from the absence of security technology.
An organisation may have several protective controls but still struggle to determine what is happening across the environment. Disconnected alerts can make it harder to identify relationships between events.
Alert overload can create another challenge. If security personnel receive large numbers of notifications without effective prioritisation, important events may compete with routine activity for attention.
There can also be an ownership gap. Detecting suspicious activity is only one part of security operations. Someone must investigate the event, determine its significance, communicate the finding, and take or coordinate appropriate action.
A managed SOC can address these operational gaps by providing a structured monitoring and escalation process.
What a Managed SOC Looks Like in a BFSI Environment
A typical managed SOC workflow begins with security information entering the monitoring environment from supported systems.
The information is then analysed for activity that may indicate a security concern. Relevant alerts are investigated using available context, and significant findings are escalated according to established procedures.
The process can be viewed as four connected activities:
- Visibility: Gather relevant security information from supported environments.
- Analysis: Examine events and identify potentially suspicious patterns.
- Investigation: Determine the significance of important alerts.
- Escalation: Communicate relevant incidents to the responsible teams for appropriate action.
The exact technologies and procedures depend on the organisation's environment and service arrangement.
What BFSI Decision-Makers Should Ask During Evaluation
A financial organisation should understand the practical boundaries of a managed SOC before entering an engagement.
Which Environments Are Covered?
The organisation should identify the systems that require security monitoring and determine whether those environments can provide the necessary security information.
Coverage should be based on business and security requirements rather than assumptions.
How Are Alerts Prioritised?
Not every security event deserves the same level of attention. The provider should explain how alerts are assessed and how potentially significant activity is distinguished from routine events.
What Happens After Detection?
The organisation needs clarity about investigation and escalation. A provider should explain what information is supplied when a significant event is communicated to the customer.
Who Takes Response Action?
Managed monitoring does not automatically mean that every response action is performed externally. Responsibilities should be defined clearly between the provider and the BFSI organisation.
How Is Performance Communicated?
Security stakeholders need meaningful operational visibility. Reporting should help them understand relevant incidents, recurring observations, and the state of security monitoring.
A BFSI Scenario: Connecting Multiple Security Signals
Imagine a financial organisation where an unusual authentication event occurs alongside other unexpected activity involving the same account.
Looking at the authentication event independently may not provide enough context. When related security signals are examined together, the organisation may have a clearer reason to investigate.
A managed SOC can support this process by analysing available security information and escalating significant findings according to the agreed workflow.
The value lies in the relationship between events and the investigation process—not simply in generating another alert.
Why Internal Security Teams May Use a Managed Model
An internal security team provides valuable knowledge of the organisation's systems, applications, users, and business processes. Yet maintaining all security-monitoring functions internally requires appropriate personnel, technology, procedures, and ongoing operational attention.
A managed SOC can complement internal resources by providing additional monitoring and security-operations capabilities.
This does not mean the external provider replaces internal ownership. Instead, responsibilities can be divided according to the agreed service model.
For example, the managed function may focus on monitoring and investigation while internal teams retain responsibility for business decisions, system changes, or specific response activities.
Clear boundaries are essential.
A Practical Selection Framework for BFSI Organisations
Before choosing a provider, security and technology stakeholders can assess the following areas:
- Business alignment: Does the service correspond to the organisation's actual security requirements?
- Monitoring coverage: Are the relevant environments supported?
- Detection process: Is there a defined approach to analysing security events?
- Investigation capability: How are important alerts examined?
- Escalation model: Are communication paths and responsibilities clear?
- Reporting: Will security stakeholders receive useful operational information?
- Integration: Can the service fit with the existing technology environment?
- Governance: Can the operating model support the organisation's broader security requirements?
This framework encourages a capability-based assessment instead of selecting a provider solely from a marketing claim.
Compliance Considerations for Indian BFSI Organisations
BFSI organisations operate under security and regulatory expectations that can vary according to the type of institution, services provided, information handled, and applicable rules.
Security monitoring can form part of a broader governance programme that includes access management, incident handling, security controls, documentation, and oversight.
Organisations should assess their specific regulatory obligations and ensure that their managed SOC arrangement supports relevant internal processes.
A managed SOC should not be viewed as a substitute for compliance governance. It is an operational component that can contribute to a broader security programme.
Avoiding a Technology-First Buying Decision
A security platform can provide valuable visibility, but the platform itself does not determine how effectively an organisation operates its security function.
For BFSI decision-makers, the more useful question is how the complete monitoring process works: what is observed, how activity is analysed, how incidents are investigated, and how findings reach the people responsible for response.
This perspective also makes provider comparisons more meaningful because it focuses on operational outcomes rather than feature lists.
Creating a More Accountable Security Operations Process
A managed SOC engagement works best when both sides understand their responsibilities.
The provider needs defined monitoring and escalation procedures. The customer needs clear ownership of systems, decisions, and response actions. Both sides need effective communication when a potentially significant security event occurs.
For Indian BFSI organisations, this clarity can make security operations more structured and easier to integrate with existing governance practices.
When assessing soc managed service providers, organisations should therefore look beyond provider labels and examine the actual operating model, security coverage, investigation process, escalation workflow, reporting, and responsibilities.
A carefully defined managed SOC relationship can become a practical part of an organisation's wider security operations strategy while allowing internal teams to retain appropriate control over their environment and security decisions.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - [email protected]