
Why Managed SOC Services India Matter for ICT Businesses
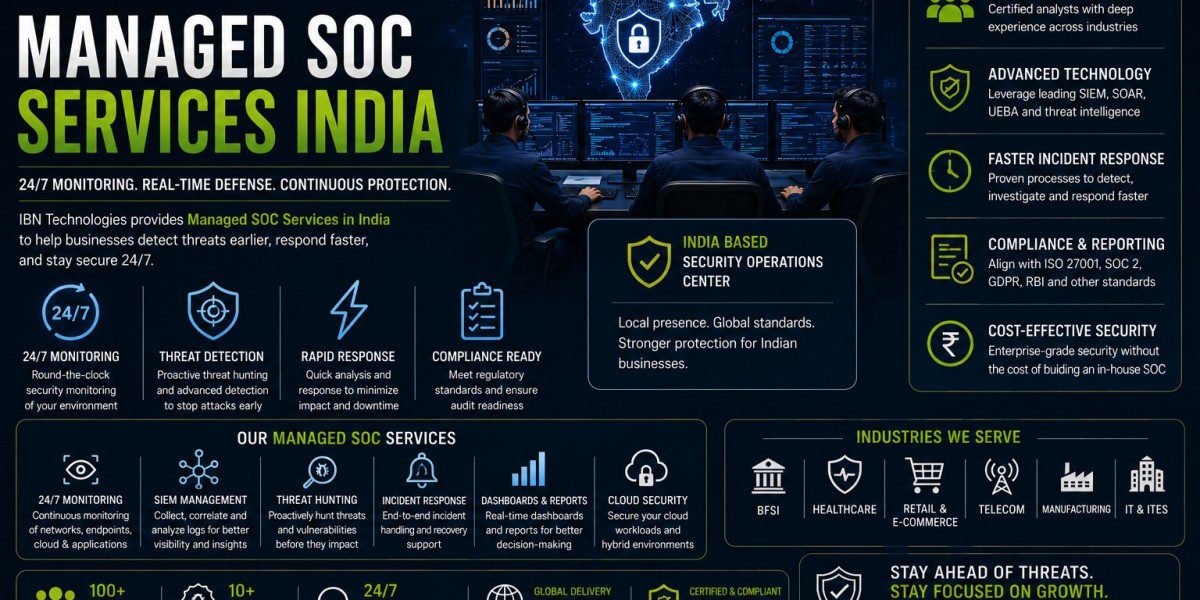
ICT businesses operate across networks, cloud environments, applications, endpoints, communication systems, and connected infrastructure. This creates a security environment where isolated monitoring can leave important activity unnoticed. managed soc services india provide an operational model in which security events can be monitored, analysed, investigated, and escalated through a dedicated security operations function.
In simple terms, managed SOC services help ICT organisations extend their security monitoring capabilities without having to build every SOC function internally. The service can bring together security visibility, alert analysis, investigation, and response coordination as part of a structured operating model.
For ICT companies, the question is therefore not simply whether a SOC is required. It is how the SOC capability should fit into the organisation's existing technology, people, processes, and security responsibilities.
Where a Managed SOC as a Service Solution Provider Fits in ICT Security
A managed soc as a service solution provider can act as an extension of an ICT organisation's internal security function. Instead of treating monitoring as a standalone technology purchase, organisations can use a managed model to support ongoing security operations.
The provider model can be particularly relevant when internal teams already manage infrastructure, applications, networks, and customer-facing technology but need additional security operations capacity. Monitoring and alert investigation can be handled through an established operational framework while internal teams remain involved in decisions that require business or technical context.
This distinction matters because effective security operations depend on more than collecting alerts. Events need to be assessed according to relevance, potential impact, and urgency before appropriate escalation takes place.
What Makes Managed SOC Services India Different From a Basic Monitoring Setup?
A basic monitoring setup may generate notifications when predefined security conditions are detected. That can provide visibility, but notification volume alone does not create an effective security operation.
Managed SOC services India can introduce a broader operational layer around monitoring. This may include reviewing security alerts, investigating suspicious activity, identifying patterns across events, prioritising incidents, and coordinating escalation.
For an ICT business, this approach can reduce the gap between detecting an event and understanding what that event means.
Consider an ICT organisation managing several customer environments. An isolated alert may appear insignificant when viewed individually. However, repeated authentication failures, unusual access behaviour, and activity across multiple systems may become more meaningful when examined together. Security operations can help connect these signals and determine whether further investigation is warranted.
How to Evaluate a Managed SOC Operating Model
Choosing a managed SOC model should begin with operational requirements rather than marketing terminology. ICT organisations can examine several practical areas before selecting a service arrangement.
Security visibility: Determine which systems, workloads, endpoints, network environments, and security sources need to contribute relevant events.
Alert handling: Understand how alerts are reviewed, categorised, prioritised, and escalated.
Investigation process: Clarify how suspicious activity is examined and how additional context is gathered.
Response coordination: Establish which actions remain with the internal ICT team and which activities the managed SOC can support.
Communication: Define how security events are communicated to technical and management stakeholders.
Operational coverage: Review whether the service model aligns with the organisation's required monitoring schedule and risk profile.
These considerations help ICT businesses evaluate a SOC as an operating capability rather than simply another security tool.
Why ICT Businesses Need Clear Roles Between Internal Teams and the SOC
Managed security works most effectively when responsibilities are clearly defined.
An ICT organisation may have infrastructure administrators, network engineers, application teams, cloud specialists, and security personnel. Each group can possess information that is important during a security investigation.
The SOC can identify and investigate suspicious activity, while internal teams can provide system context and carry out approved technical or business actions. Clearly documented escalation paths help prevent delays when an event requires immediate attention.
This collaborative structure also makes it easier to distinguish between security monitoring responsibilities and broader IT operations.
The value of managed soc as a service solution provider becomes clearer when the organisation understands exactly where the external security operation begins, where internal ownership remains, and how the two teams communicate.
Benefits of Managed SOC Services for ICT Security Operations
A structured managed SOC model can support ICT organisations in several areas.
- Continuous security oversight: Security events can be monitored through an organised operational process.
- Improved alert prioritisation: Relevant events can receive greater attention than routine or low-value notifications.
- Security investigation support: Suspicious activity can be examined using available event information and context.
- Operational scalability: Security monitoring can expand alongside changing technology environments.
- Defined escalation: Security events can move through predetermined communication and response paths.
- Better visibility: Bringing security events into a coordinated monitoring process can help teams understand activity across different technology layers.
These benefits depend on the quality of the operating model, available security data, defined responsibilities, and how consistently the service is integrated with internal processes.
An ICT Example: Connecting Security Events Across a Distributed Environment
Imagine an ICT company operating a combination of enterprise applications, network infrastructure, cloud resources, and remote access services.
A suspicious login might initially appear to be a routine authentication event. A second signal involving unusual access to a sensitive system could change its significance. If security events are reviewed independently, the relationship between them may be missed.
A managed SOC can provide a central operational point for reviewing these events and determining whether they represent a broader security concern.
The internal ICT team can then provide additional system knowledge and support the appropriate response. This division of responsibilities allows technical teams to continue managing their core environments while security operations maintain focus on monitoring and investigation.
Practical Checklist Before Adopting Managed SOC Services India
Before implementing managed SOC services India, ICT organisations should document:
- Critical systems and environments requiring monitoring
- Security event sources available for analysis
- Internal security and IT responsibilities
- Alert escalation requirements
- Incident communication procedures
- Required monitoring coverage
- Investigation and reporting expectations
- Access and data-handling requirements
- Governance and compliance obligations
- Processes for reviewing service effectiveness
This preparation can make the transition into a managed security operating model more structured and measurable.
Security Governance and Compliance Considerations for ICT Businesses
Security monitoring should also support the organisation's broader governance framework. ICT businesses may need to demonstrate that security controls are documented, monitored, reviewed, and supported by appropriate evidence.
A managed SOC can contribute operational information that helps security teams understand events and maintain records for internal reviews. However, security monitoring should not be treated as a replacement for governance, risk management, access controls, policies, or other security responsibilities.
The organisation should establish how monitoring activities connect with its existing security framework and applicable requirements.
As ICT environments continue to become more distributed, security operations need to keep pace with the systems and services being introduced. managed soc services india can provide a structured approach to monitoring, alert analysis, investigation, and escalation while allowing internal technology teams to retain their operational responsibilities. The right model ultimately depends on the organisation's environment, security requirements, internal capabilities, and clearly defined operating processes.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - [email protected]