
A Practical Guide to SOC SIEM Consulting in India for Growing ICT Operations
ICT businesses support highly connected environments where networks, communications platforms, cloud services, applications, endpoints, and customer-facing technologies can operate together.
As these environments become more interconnected, security teams need visibility across more than individual systems. They need to understand how security events relate to one another and how the organisation should respond when suspicious activity is detected.
This is where soc siem consulting can help ICT businesses make more informed decisions about security operations.
Rather than beginning with a technology purchase, consulting can help an organisation understand its monitoring requirements, security data sources, operational gaps, and response responsibilities.
That approach is particularly relevant for ICT organisations where technology infrastructure and service environments can change frequently.
What SOC SIEM Consulting Brings to ICT Security
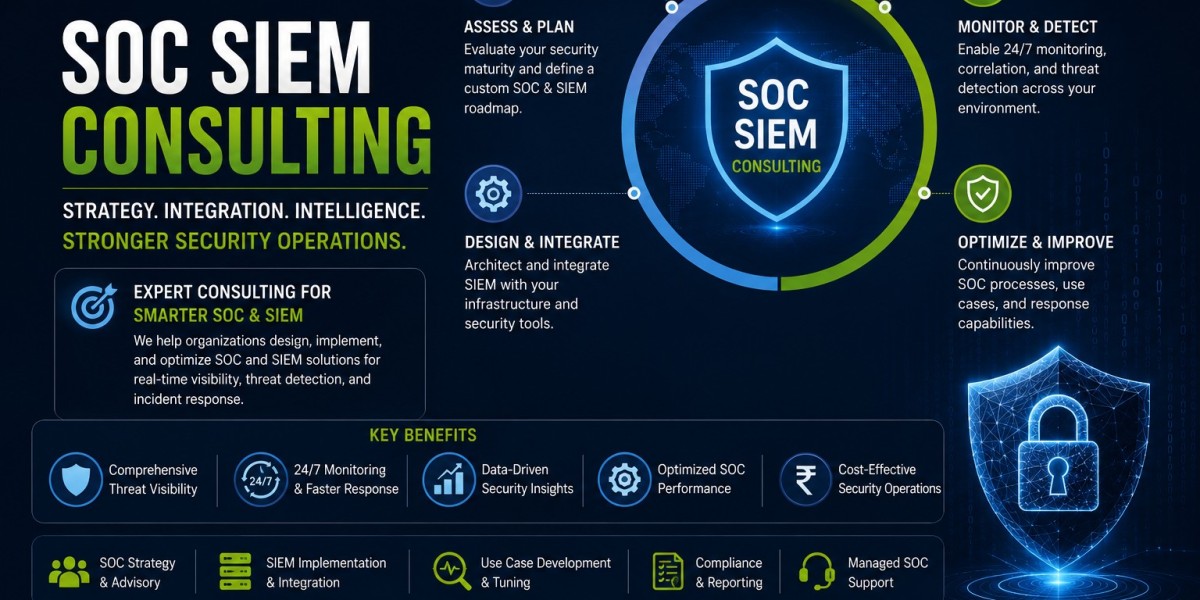
SOC SIEM consulting helps ICT organisations assess and align SIEM technology, SOC monitoring, threat detection, investigation, and response processes with their technology environment and operational requirements.
The goal is to create a connected security operation.
SIEM can centralise and analyse security information from relevant sources, while SOC functions provide monitoring, investigation, escalation, and response coordination.
Consulting helps determine how those capabilities should work together.
For ICT businesses, this can be important because security requirements often extend across multiple technology environments rather than a single infrastructure layer.
Why a Managed SOC Service Needs the Right Operational Fit
An ICT organisation considering a managed soc service should evaluate more than whether continuous monitoring is available.
The service needs to fit the organisation's architecture, internal responsibilities, security processes, and expected growth.
For example, an ICT business may operate cloud infrastructure alongside on-premises systems and network environments. Its security monitoring model should account for the relevant events generated across those environments.
The organisation should also understand how alerts are investigated, how incidents are escalated, and how security findings are communicated to internal teams.
A managed service becomes more useful when it complements existing security operations rather than operating independently from them.
The ICT Security Challenge Is Often About Visibility
ICT businesses can have many security technologies in place and still face visibility gaps.
Security events may be generated by network infrastructure, cloud systems, applications, endpoints, authentication services, and other components.
When these signals remain separated, identifying broader patterns can become difficult.
SIEM can help bring relevant security information into a centralised analytical environment.
This creates an opportunity to correlate events and identify relationships that may not be obvious when individual logs are reviewed separately.
However, centralisation alone is not enough.
The organisation also needs processes for determining which events require attention and what should happen when suspicious activity is identified.
Why Buying More Security Tools May Not Solve the Problem
Adding another security product does not automatically create better security operations.
ICT organisations may already have several technologies producing security information. If those tools operate without a coordinated monitoring and investigation process, the organisation can still struggle to determine what matters.
This can lead to duplicated alerts, inconsistent investigations, or excessive manual review.
A consulting approach starts from the security objective rather than the product.
The organisation first identifies what it needs to monitor, what information is important, which events represent potential risk, and how the response process should work.
Technology can then be aligned with those requirements.
Where SOC SIEM Consulting Creates Practical Value
Consulting can support ICT organisations across several areas:
- Security environment assessment
- SIEM planning and event visibility
- Monitoring requirements
- Threat detection processes
- Alert investigation
- Incident escalation
- Response coordination
- Security reporting
- Operational improvement
The exact scope depends on the organisation's technology environment and security objectives.
Understanding the Difference Between SIEM and SOC
The terms SIEM and SOC are sometimes used together, but they serve different functions.
SIEM is a technology capability used to collect, analyse, and correlate security information.
A SOC is an operational function responsible for monitoring security activity, investigating suspicious events, supporting threat detection, coordinating incident response, and reporting security activity.
They work well together because the SOC needs reliable security information to monitor and investigate.
An ICT organisation should therefore avoid treating SIEM implementation as the complete answer to its security operations requirements.
The technology and operating model should be planned together.
What ICT Businesses Should Assess Before Selecting a Service
Before selecting a SOC or SIEM approach, ICT organisations should understand their own environment.
The assessment should consider which systems are business-critical, where relevant security data originates, how security incidents are currently handled, and where monitoring gaps exist.
It should also consider how the environment is expected to evolve.
An ICT business expanding its cloud presence may have different requirements from one primarily operating traditional network infrastructure.
Similarly, an organisation with an established security team may require a different service model from one that needs greater external operational support.
Understanding these differences makes service evaluation more meaningful.
Comparing Security Operations Capabilities
A structured comparison can help ICT businesses assess whether a SOC and SIEM approach matches their needs.
Evaluation Area | Questions ICT Businesses Should Consider |
Monitoring | Does the service provide visibility appropriate to the organisation's operating environment? |
SIEM | Can relevant security data be collected, analysed, and correlated effectively? |
Threat Detection | How are potentially suspicious events identified and investigated? |
Response | How are incidents escalated and coordinated with internal teams? |
Environment | Can monitoring support relevant cloud, on-premises, and hybrid infrastructure? |
Reporting | Will security information be presented clearly to technical and management stakeholders? |
Integration | Can the service work alongside existing security processes and teams? |
Scalability | Can the model adapt as infrastructure, applications, and users change? |
The purpose of this comparison is not simply to identify the longest feature list. It is to determine whether the security operating model is appropriate for the organisation.
Creating Clear Roles Between Internal Teams and the SOC
A managed security operation works more effectively when responsibilities are defined before an incident occurs.
The internal ICT team may retain responsibility for infrastructure, applications, identity, access, or business decisions. The SOC may monitor events, investigate alerts, identify suspicious activity, and escalate incidents.
These responsibilities should be understood by everyone involved.
Without clear ownership, an alert can move between teams without a defined decision-maker.
Consulting can help organisations document these operating relationships and establish appropriate escalation processes.
How SIEM Supports a More Connected View
An ICT environment can generate security information from many different sources.
A centralised SIEM can help security teams bring relevant data together for analysis.
This can make it easier to identify relationships between events occurring across different systems.
For instance, separate events involving authentication, network activity, and endpoint behaviour may provide greater context when examined together than when each is viewed independently.
The objective is not to correlate every event automatically.
The objective is to provide security teams with useful information that supports investigation and decision-making.
Incident Response Should Be Planned Before an Alert
A security team should not have to design its response process while dealing with an active incident.
ICT organisations should establish escalation paths and communication responsibilities in advance.
When suspicious activity is detected, teams should understand who investigates, who owns the affected technology, who makes business decisions, and how relevant information is communicated.
A managed SOC can support this process, but the internal organisation still needs clearly defined responsibilities.
The combination of external monitoring and internal ownership can create a more practical response model.
Reporting Should Support Better Security Decisions
Security reporting should translate operational activity into information that stakeholders can understand.
Technical teams may need details about alerts, affected systems, investigations, and response activity.
Management may need a broader view of security trends, recurring issues, and areas requiring attention.
A useful reporting process should support both perspectives.
For ICT businesses, this can make SOC activity more closely connected to broader technology governance rather than treating security monitoring as an isolated technical function.
A Practical Review Before Choosing a SOC Model
ICT organisations can use the following review points before selecting or redesigning their SOC and SIEM approach:
- Map the technology environments that require security monitoring.
- Identify the main sources of security logs and events.
- Review current SIEM capabilities and limitations.
- Identify recurring alert-investigation challenges.
- Define which events require escalation.
- Clarify internal and external security responsibilities.
- Review existing incident response and communication procedures.
- Determine what security reporting different stakeholders require.
- Consider how monitoring needs may change as the ICT environment expands.
This exercise can reveal whether the organisation needs new technology, additional operational capacity, improved processes, or a combination of these.
Preparing for an ICT Environment That Keeps Changing
ICT businesses operate in environments where infrastructure and services can evolve rapidly.
New applications, cloud services, network changes, integrations, and remote access arrangements can all affect security monitoring requirements.
A SOC and SIEM strategy should therefore be reviewed as the environment changes.
Consulting can help organisations reassess monitoring coverage and operational processes rather than treating the initial security design as permanent.
This makes the security model more adaptable and reduces the risk of creating monitoring gaps as technology develops.
Turning Service Selection Into a Security Strategy
Choosing a managed security service should not be separated from the organisation's broader security strategy.
ICT businesses need to understand what they want the service to accomplish, what responsibilities will remain internal, which systems require monitoring, and how incidents will be handled.
This makes the evaluation process more useful than simply comparing providers by features.
The right questions are operational:
What needs to be monitored?
How should security information be analysed?
Which events matter most?
Who investigates them?
Who responds?
How will management understand the results?
Answering these questions provides a stronger basis for selecting a security operating model.
Building a Better-Fit Security Operation
ICT organisations need security operations that can keep pace with connected technology environments.
Soc siem consulting can help bring together the strategic and operational considerations behind SOC and SIEM adoption, from security visibility and monitoring to investigation, response, reporting, and scalability.
For businesses considering a managed SOC model, the emphasis should remain on operational fit rather than technology alone.
A well-defined security approach can help ICT teams understand their environment more clearly, establish appropriate monitoring priorities, and create stronger coordination between internal teams and external security operations.
As ICT infrastructure continues to evolve, a security strategy built around visibility, defined responsibilities, continuous monitoring, and structured response can provide a more sustainable foundation for managing security risk.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - [email protected]