
Choosing a Managed SOC as a Service Partner Without Guesswork
Indian ICT businesses operate across networks, communication systems, cloud platforms, applications, connected devices, and customer-facing services. As these environments become more interconnected, security teams need to detect suspicious activity quickly and understand what is happening across multiple technology layers. managed soc as a service can provide an external security operations capability for organizations that need continuous monitoring without creating every SOC function internally.
However, choosing a provider should involve more than comparing service descriptions. The quality of the operating model, monitoring coverage, response process, reporting, and coordination with internal teams can significantly affect how useful the service becomes.
What should an ICT business expect from managed SOC as a service?
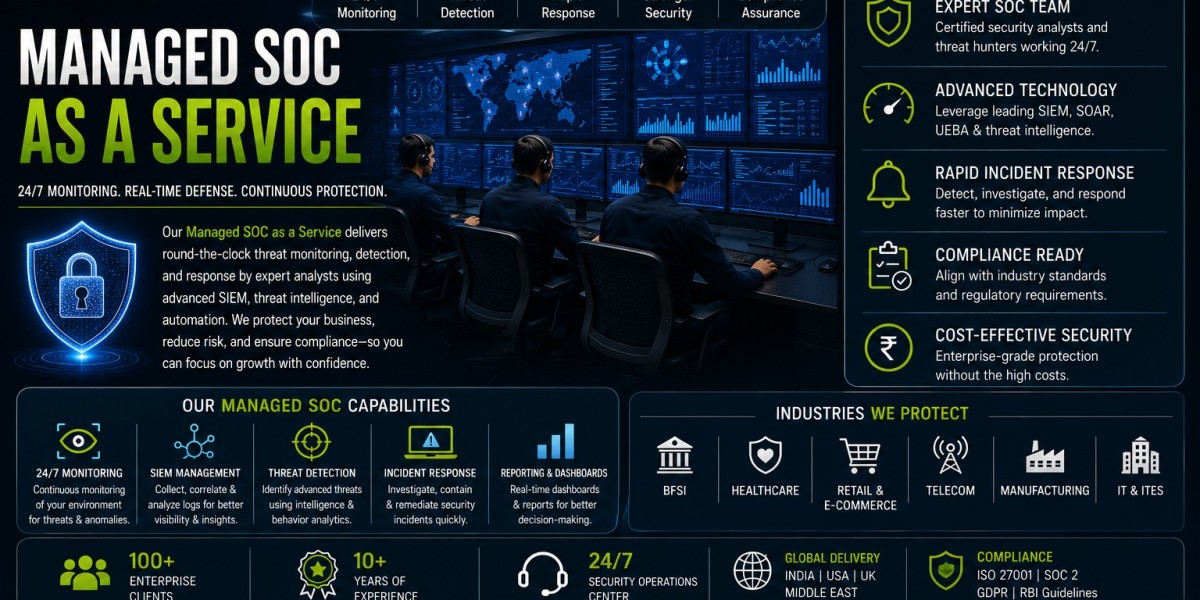
Managed SOC as a service provides ongoing security monitoring, threat detection, investigation, and response support through an external security operations function. Instead of relying solely on internal personnel to monitor security events, an organization can use a managed service to analyze activity, identify potential threats, escalate relevant incidents, and maintain security reporting.
For ICT organizations, this model can be particularly relevant because technology environments often contain many interconnected systems. A security event affecting one component may have implications for other parts of the infrastructure.
A managed SOC can help establish a consistent process for collecting security information, analyzing events, investigating suspicious behavior, and coordinating response.
How should an ICT company assess a managed SOC as a service solution provider?
A provider should be evaluated according to how its services fit the organization's actual security environment. managed soc as a service solution provider should be more than a label used to describe outsourced monitoring; the organization should understand the specific operational capabilities being delivered.
Questions around monitoring coverage, incident handling, escalation, reporting, threat detection, and security expertise can reveal whether the service is designed for the organization's requirements.
For example, an ICT company with extensive network infrastructure may require strong network security visibility, while an organization with a large cloud footprint may need broader monitoring across cloud workloads and connected applications.
The evaluation should therefore start with the organization's technology environment rather than the provider's feature list.
What happens when a security alert is detected?
This is one of the most important questions an ICT business can ask.
An alert may indicate suspicious activity, but it does not automatically explain its severity or cause. A useful SOC operation needs a process for analyzing the event, establishing context, determining whether escalation is necessary, and supporting an appropriate response.
The provider should be able to explain this workflow clearly. Ambiguity around responsibilities can slow down incident handling when an event requires immediate attention.
Why is monitoring coverage important for ICT organizations?
ICT environments can span network infrastructure, endpoints, applications, cloud platforms, security devices, and other connected systems. Monitoring only one part of this environment can leave gaps in visibility.
A managed SOC should therefore be evaluated according to the systems and data sources it can monitor and analyze.
Security visibility also needs context. A suspicious login, unusual network connection, or unexpected system change may appear insignificant when viewed independently but become more meaningful when correlated with other events.
Centralized security monitoring can help security teams investigate these relationships more effectively.
Which provider capabilities matter beyond 24/7 monitoring?
Continuous availability is useful, but "24/7 monitoring" alone does not describe the full quality of a managed SOC service.
An ICT business should examine how the provider approaches threat detection, investigation, threat hunting, incident response, reporting, and compliance monitoring.
IBN Technologies' managed SIEM and SOC services include continuous security monitoring, threat detection, threat intelligence, threat hunting, incident response and forensics, security device monitoring, policy and compliance monitoring, and user behavior analytics.
These capabilities represent different stages of security operations. Monitoring identifies activity, detection highlights potential threats, investigation adds context, and response processes help organizations address relevant incidents.
Why does reporting matter when selecting a managed SOC?
Security leaders need more than a stream of technical notifications. They need information that helps them understand what happened, why it matters, what actions were taken, and whether recurring security issues require attention.
Useful reporting can also support internal governance and security reviews. It can provide a record of incidents, investigations, monitoring activity, and relevant security observations.
For ICT businesses, reporting should be understandable to both technical teams and business stakeholders. A report that cannot communicate risk or required action clearly has limited operational value.
How can a managed SOC work alongside an internal ICT team?
A managed SOC should complement internal teams rather than create confusion about ownership.
Before onboarding a provider, the organization should establish clear responsibilities. The external SOC may monitor and investigate security events, while internal teams may remain responsible for infrastructure changes, remediation, business decisions, or specific response actions.
Escalation procedures should identify who receives high-priority incidents and how quickly the relevant internal stakeholders need to become involved.
This division of responsibility becomes particularly important during a serious security event. Internal teams should not have to determine basic roles while an incident is already developing.
What are the risks of choosing a provider based only on price?
Cost is a legitimate consideration, but selecting a managed SOC solely on price can overlook important operational differences.
Two providers may both advertise continuous monitoring while offering different levels of threat analysis, investigation, reporting, response support, and technology coverage.
ICT organizations should therefore compare the scope of the service rather than looking only at the commercial figure.
The evaluation should consider whether the provider can support the organization's current environment, whether the service can adapt as infrastructure changes, and whether responsibilities are clearly defined.
What should an ICT business check before onboarding a provider?
A practical evaluation can focus on several areas:
- Security monitoring coverage
- Supported security data sources
- Threat detection and investigation processes
- Incident escalation procedures
- Response and forensic capabilities
- Threat hunting
- Security reporting
- Policy and compliance monitoring
- Integration with internal IT and security teams
- Scalability as the technology environment changes
These factors help organizations assess the actual operating model behind a managed SOC service.
How does managed SOC support ICT security governance?
Security operations can contribute to governance by creating structured processes for monitoring, investigation, incident handling, and reporting.
IBN Technologies provides managed security services that include compliance-oriented monitoring and reporting aligned with applicable standards and regulatory requirements, including ISO 27001 and CERT-In. The relevant requirements vary depending on the organization, its services, infrastructure, and applicable regulations.
For ICT businesses, governance becomes more practical when security operations generate consistent evidence and reporting. This can help security and compliance teams understand whether monitoring and response processes are operating as expected.
Frequently Asked Questions
What is a managed SOC as a service solution provider?
A managed SOC as a service solution provider delivers outsourced security operations such as continuous monitoring, threat detection, investigation, reporting, and response support. The provider works as an external security operations function for the organization.
What should an ICT company ask a managed SOC provider?
An ICT company should ask about monitoring coverage, threat detection, investigation, escalation, response procedures, reporting, technology compatibility, and responsibilities between the provider and internal teams.
Can a managed SOC support cloud-based ICT environments?
A managed SOC can support organizations with distributed technology environments when the service has appropriate visibility into relevant cloud, network, endpoint, application, and security data sources. The required coverage depends on the organization's infrastructure.
Is continuous monitoring enough to provide effective security?
Continuous monitoring is an important component, but effective security operations also require analysis, investigation, escalation, response, and reporting. Monitoring becomes more valuable when security events are turned into actionable findings.
Selecting a managed SOC provider is ultimately an operational decision, not simply a technology purchase. For Indian ICT organizations, the right evaluation should focus on visibility, detection, investigation, response, reporting, and how the external security function will work with internal teams.
managed soc as a service can provide a structured security operations layer when the service scope matches the organization's infrastructure and responsibilities. A careful provider evaluation helps ensure that continuous monitoring translates into meaningful security operations rather than simply producing more alerts.
Contact Us:
IND- 02067680404
IBN Technologies Ltd.
E-mail: - [email protected]